Blog
Major Upgrades to Watchful’s Vulnerability Scanner
Watchful’s vulnerability scanner gets a major upgrade with new malware and reputation checks, CVE detection, automated scanning, and intelligent security notifications.
Watchful’s vulnerability scanner gets a major upgrade with new malware and reputation checks, CVE detection, automated scanning, and intelligent security notifications.

Content Security Policy, usually abbreviated as CSP, is an HTTP response header that allows a website to tell browsers which sources and behaviors should be permitted when displaying its pages. A complete CSP can control many different aspects of a website. However, you do not need to implement a complicated Read more
HTTP Strict Transport Security, usually abbreviated as HSTS, is a security header that tells web browsers to access your website using HTTPS only. Once a browser receives an HSTS header from your website, future attempts to visit the site over HTTP are automatically upgraded to HTTPS. The browser will also Read more
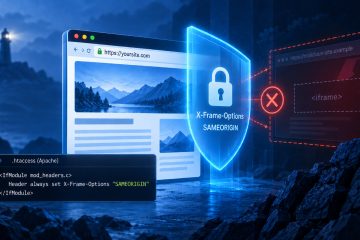
The X-Frame-Options HTTP response header helps control whether pages from your website can be displayed inside a frame or iframe on another website. If this header is missing, another site may be able to embed your pages inside its own content. This can increase the risk of clickjacking, where a Read more
PHP is the programming language that powers WordPress. Depending on your server configuration, the exact version of PHP running your website may be included in its HTTP response headers. For example, your server might return: X-Powered-By: PHP/8.2.33 Visitors do not normally see HTTP response headers when browsing your website, but Read more
Learn how to investigate a suspected hacked WordPress or Joomla! website, identify malicious changes, remove malware, and secure your site against future attacks.
Firewalls sometimes block legitimate services and trusted visitors. Learn how to allowlist IP addresses in Cloudflare, hosting firewalls, and WordPress or Joomla! security tools without unnecessarily weakening your website’s protection.
Learn why your website’s IP address may change, how to check whether the change is expected, and how to troubleshoot unexpected or repeated IP address changes.
WordPress includes a built-in debugging system that can help identify problems with plugins, themes and custom code. When debug logging is enabled using the default settings, WordPress typically writes PHP errors, warnings and notices to: wp-content/debug.log The information in this file can be extremely useful when troubleshooting a website. Unfortunately, Read more
If you read this blog, you’ll know that we take website security very seriously. And we always recommend using the Cloudflare service as one of the tools in your security toolbox. In this post we will share a simple Cloudflare hack that blocks many of the WordPress brute-force attacks your Read more